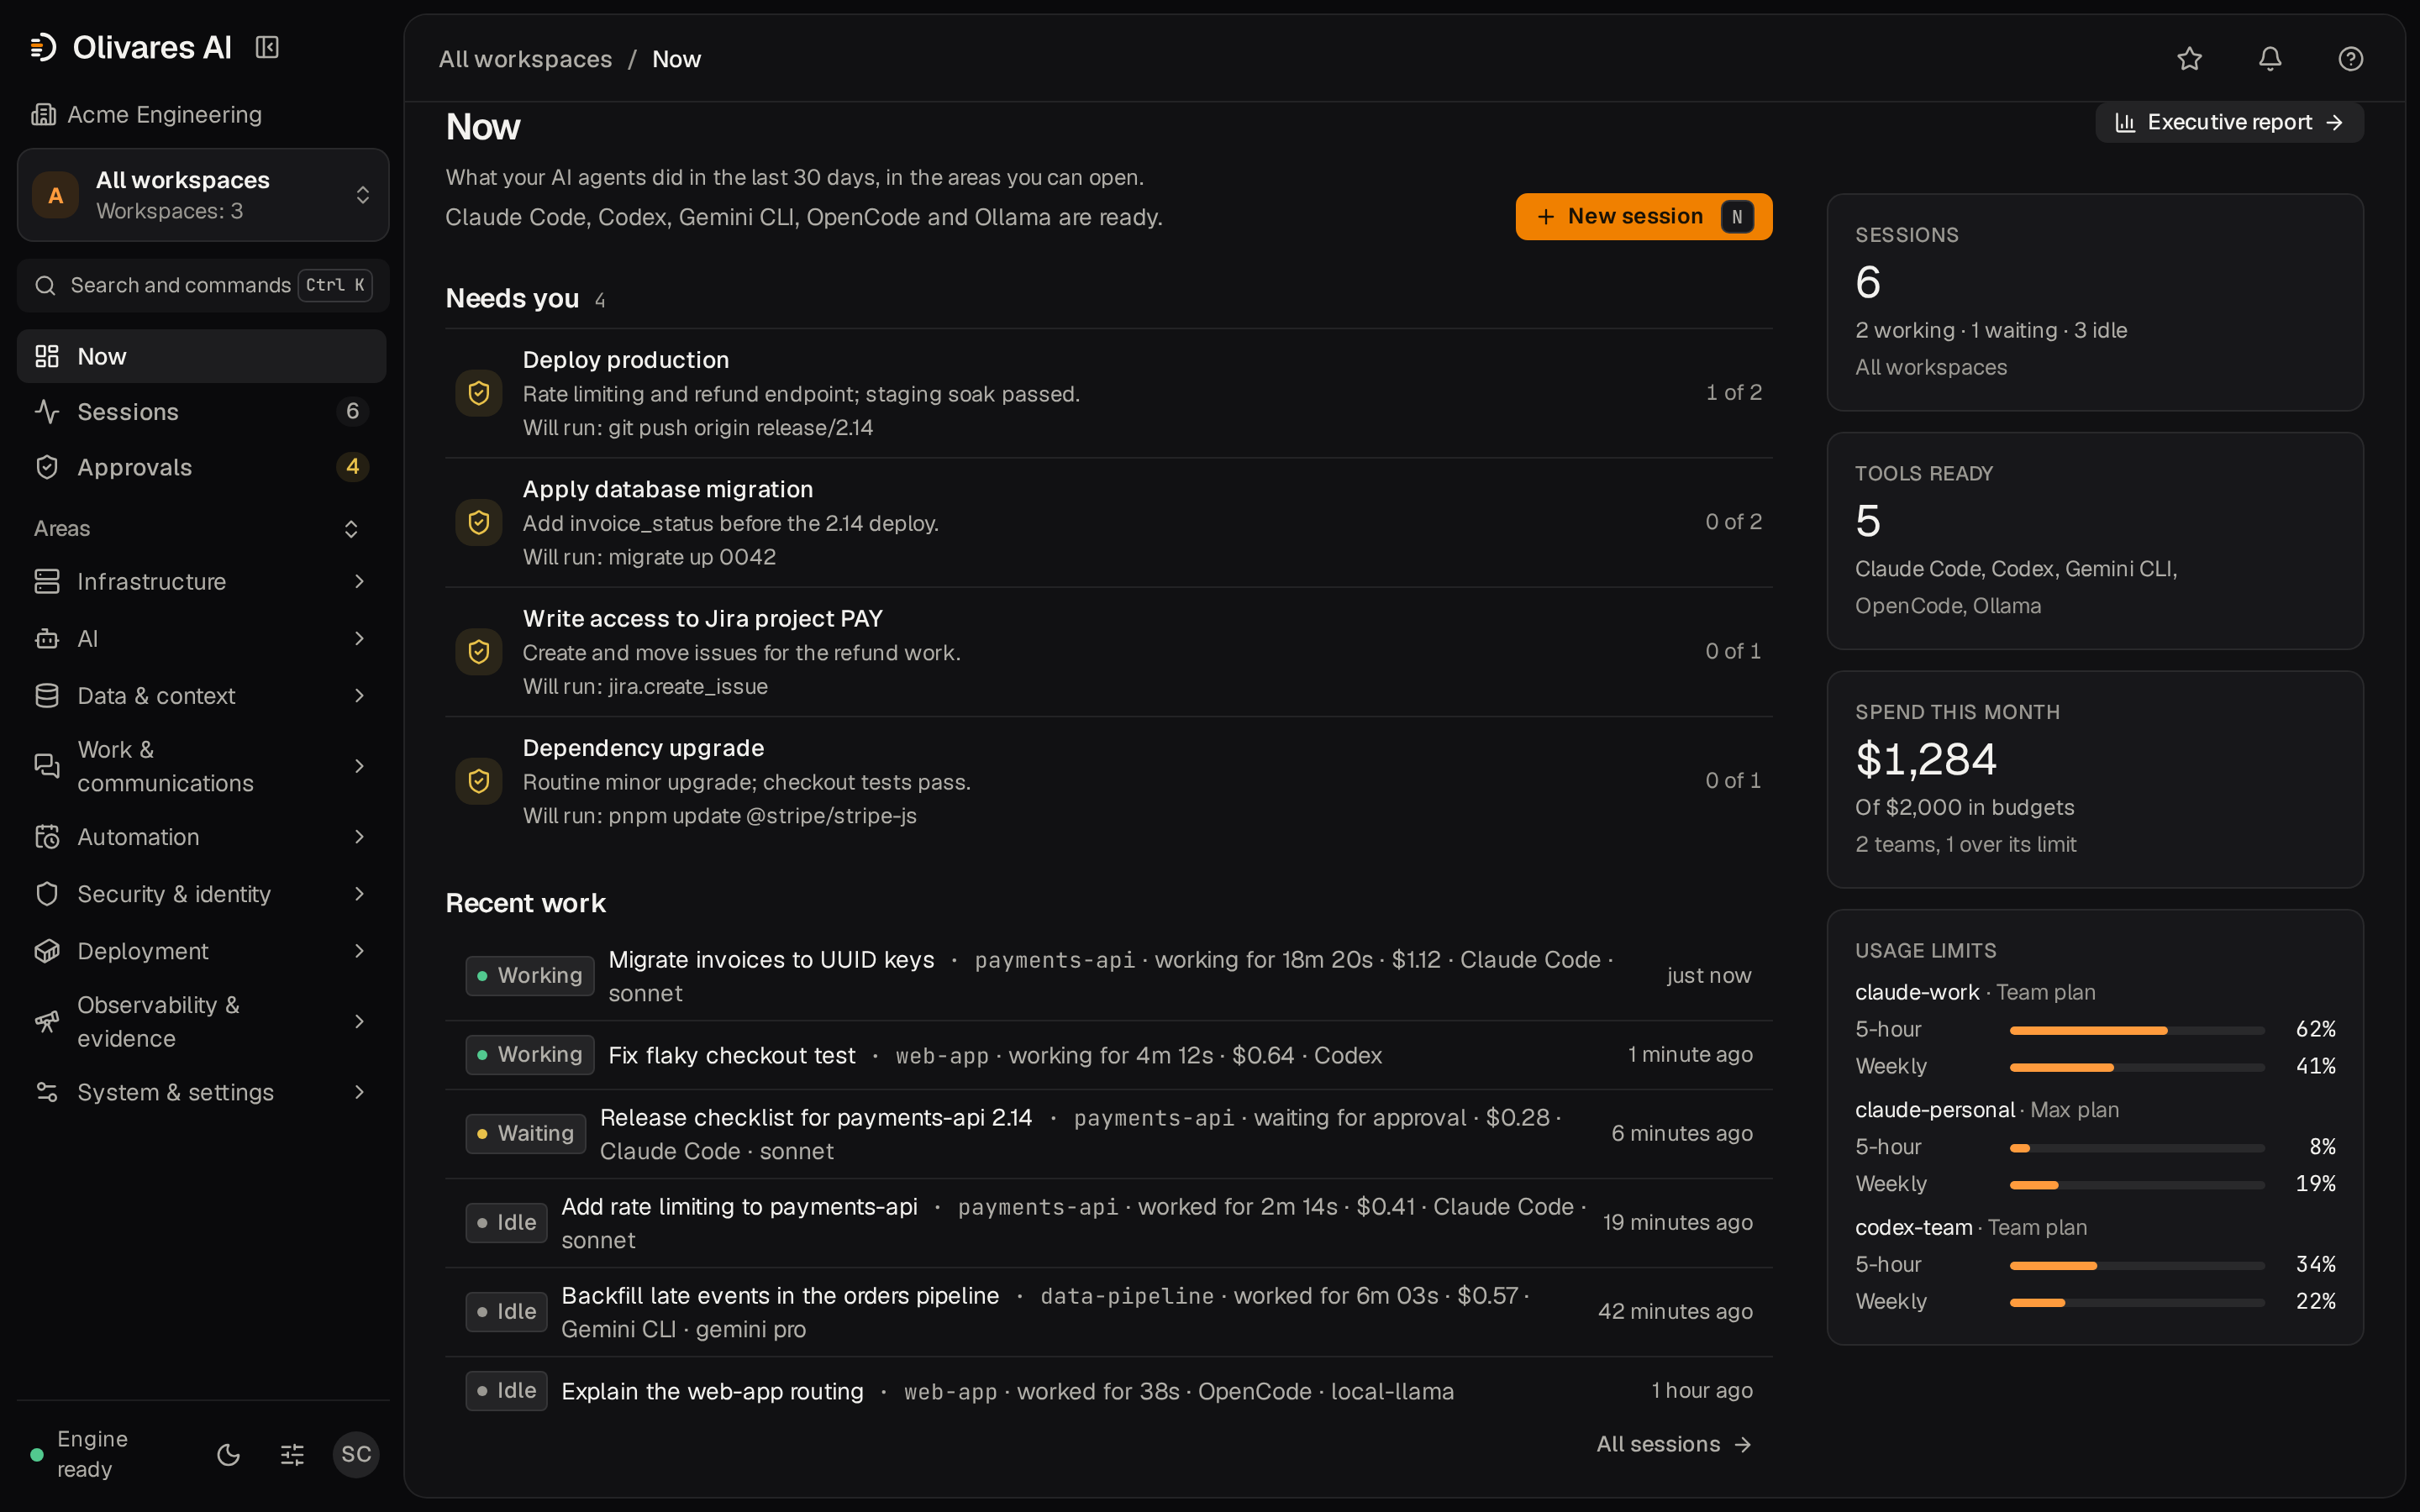
Run Claude Code, Codex and Grok on your own server, from the browser
Start, follow, approve and stop Claude Code, Codex and Grok sessions on a server you own, from a web console or the CLI, with your existing accounts.
Technical notes on running, governing and auditing AI tools on infrastructure you run.
Start, follow, approve and stop Claude Code, Codex and Grok sessions on a server you own, from a web console or the CLI, with your existing accounts.
How a hash-chained ledger with per-event Ed25519 signatures and OSCAL export produces audit evidence an external verifier can confirm independently.
Static API keys never expire, share identity, and silently shadow federation. WIF replaces them with attested JWT exchange for short-lived per-session tokens.
How a PEP classifies every Claude Code hook event into gating, context, or observe, wires the correct output schema per event, and deny-closes unknown events.
Trace the OAuth 2.1 flow MCP mandates after a protected server returns 401, what RFC 9728 and RFC 8707 provide, and the security pitfalls.
Drift between what an AI agent is permitted to do and what it is observed doing becomes a structured, classified finding with confidence levels.
Anthropic's apps gateway handles OIDC auth for Claude. Your estate is more than Claude. This is the co-deployment architecture that governs both paths.
An AI agent holds credentials, is permitted some actions, and is observed doing others. The access map shows the gap, and where least-privilege quietly broke.
Build an auditor-grade trail for Claude Code and MCP servers without leaving your perimeter: per-agent identity, a hash-chained ledger, untrusted MCP signals.
How to spot least-privilege drift in AI agents by comparing permitted access with observed behavior and enforcing policy at access time.
Why self-hosting an AI platform is the strongest data-residency posture under GDPR: the governance tool never receives your data. Edges, not payloads.
Two ways to see your AI agents: an inline proxy with high blast radius, or passive discovery from logs, OpenTelemetry and an eBPF backstop. An honest tradeoff.