Product · Identity & NHI
Give every agent its own identity — and know when it doesn’t
A shared service account makes "which agent did this?" unanswerable. Olivares binds an agent to a non-human identity, mints a dedicated per-agent NHI, and surfaces the agents that are sharing one — the difference between attributing access firmly and only approximately. An identity it cannot resolve is never quietly treated as a real one. The identity inventory and agent bindings are Community; directory and roster connectors, agent identity federation and PIV/CAC are Business (Identity & Scale). Agent registration is Business (Identity & Scale).
In the product
Identity and access
Example data. The user sources people sign in from, every user with their groups, role and sign-in method, and the groups mapped to roles. Several user sources and group-to-role mapping are Business (Identity & Scale).
What you govern
From a shared account to a per-agent identity
Identity is the axis the access map attributes on. A dedicated NHI per agent turns "approximately" into "firmly"; everything below is honest about how far it can get.
Bind or mint an NHI
Bind an agent to an existing non-human identity, or mint a dedicated per-agent NHI. A dedicated NHI is what lets the access map attribute access firmly to one agent — not approximately to a pool.
Shared-identity finding
When more than one agent rides the same account, per-agent attribution is genuinely ambiguous. Olivares surfaces that as a finding and says so — it does not split the difference and pretend it knows which agent acted.
Read-only WIF graph
The honest unknown
An identity Olivares cannot resolve is drawn as unknown and flagged — never silently promoted to a named NHI. No identity signal means no attribution, stated plainly.
How it works
Agent identity records and declared relationships
Creating an NHI adds a per-agent identity record in Olivares. That record does not itself issue a SPIFFE credential or establish federation. This diagram illustrates declared relationships; an unresolved identity remains unknown.

What’s real
Identity records, configurable step-up and federation visibility
The read-only WIF graph starts from configured federation rules. With a configured Anthropic WIF connection and an org:admin OAuth token, Olivares compares those rules with live federation configuration and shows provenance and drift. Without that token it shows declarations only; a failed live query is shown as unavailable. This does not prove federation with every identity provider. Agent identity federation is Business (Identity & Scale).
- Shipped as read-only ingestion: roster connectors read the hyperscaler agent-identity registries — Microsoft Entra Agent ID, AWS Bedrock AgentCore and Google’s agent registry. Live-verified federation on the wire against them remains on the roadmap, and we do not claim it before it ships.
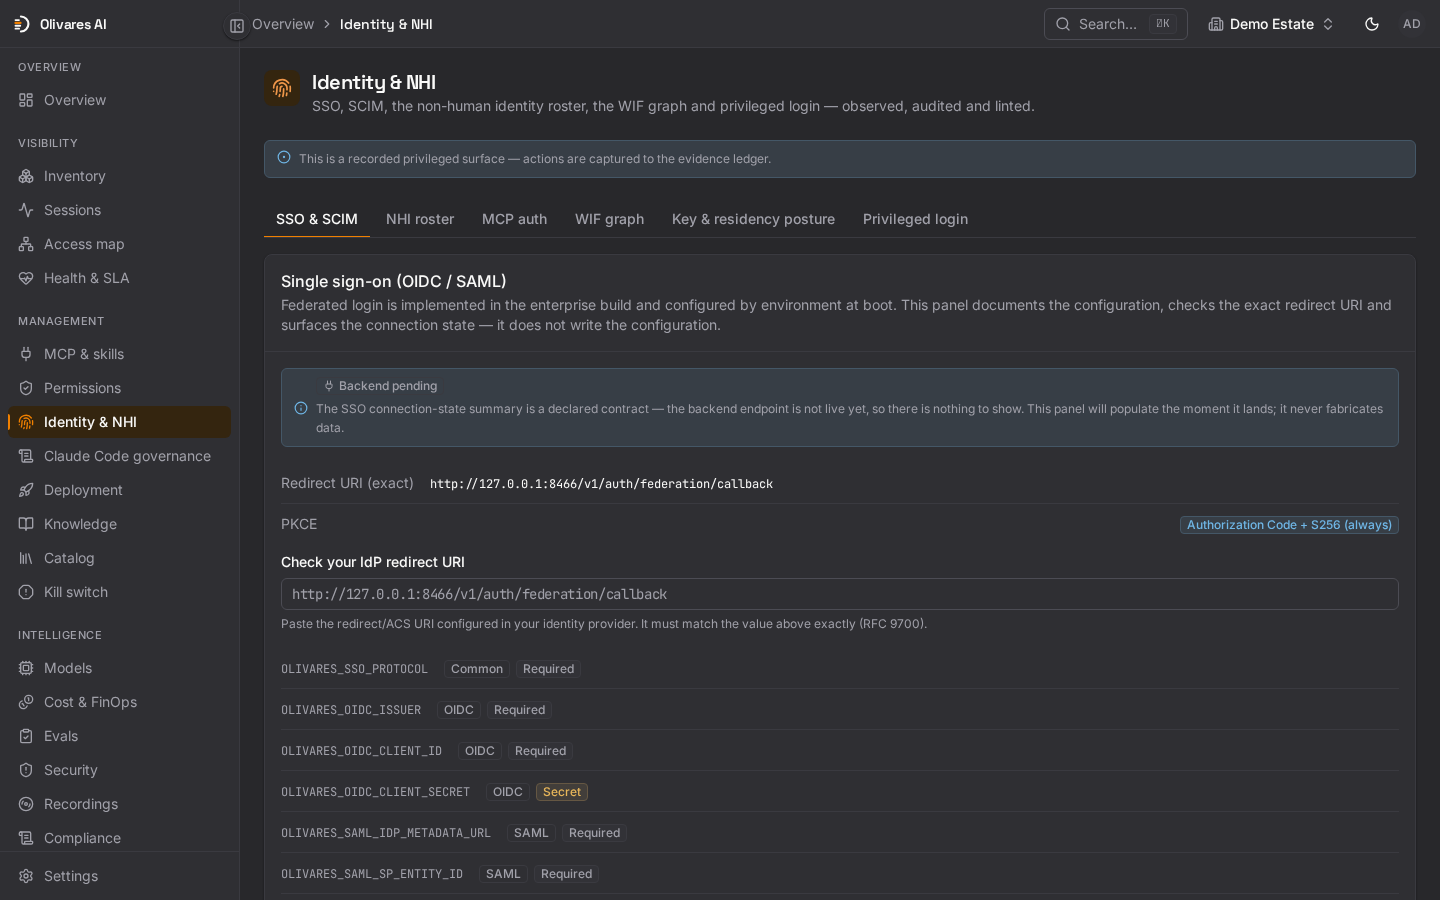
- Community includes one active OIDC or SAML identity provider. Business: Identity & Scale adds the inbound SCIM 2.0 server for users and groups, multiple identity providers and enforced SSO policy.
Business: directories and several identity providers
Community signs in with one OIDC or SAML provider. Business adds the inbound SCIM 2.0 server, up to five active identity providers, directory import from Okta, Entra ID, Keycloak and others, departments, SCIM provisioning out and PIV/CAC step-up.
Identity & NHI — questions
Does Olivares federate live with Entra Agent ID, AWS AgentCore or Google Agent Identity today?
Two agents share one service account. Which one does Olivares say acted?
Neither, firmly. A shared identity makes per-agent attribution genuinely ambiguous, so Olivares raises a shared-identity finding and attributes access only approximately — it will not fabricate certainty about which agent acted. Mint a dedicated per-agent NHI and the access map can then attribute that agent firmly.
Do you support WebAuthn AAL3 or PIV-CAC step-up for privileged logins?
Olivares supports WebAuthn/FIDO2 and PIV/CAC. The administrator chooses the extra assurance policy: none (the default, no additional ceremony), totp (authenticator code or supported identity-provider MFA), or passkey (fresh passkey or PIV verification). Break-glass and critical approvals follow that policy. Authentication, permissions and tenant isolation still apply. AAL3 is an assurance target, not a NIST or FIPS certification. PIV/CAC and break-glass are Business.
Do Community and Business include SSO and SCIM provisioning?
Community includes one active OIDC or SAML identity provider. Business: Identity & Scale adds the inbound SCIM 2.0 server for users and groups, multiple identity providers and enforced SSO policy.
Give your agents identities you can attribute
Deploy Olivares on your own infrastructure, mint a dedicated NHI per agent, and turn "approximately" into "firmly" on your access map.